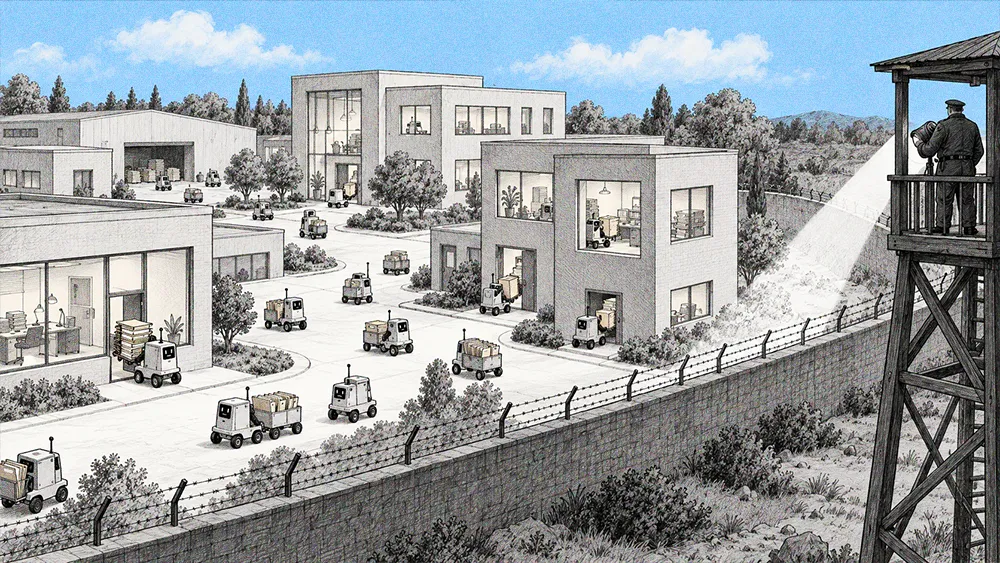

Everyone is talking about governing their agents, but where is the control plane that monitors an agent's behavior and reports it to the enterprise threat management function?
 Vipin VarmaSVP, CISO & Head Cybersecurity Practice, CitiusTech
The views and opinions expressed are those of Vipin Varma and do not represent the official policy or position of any organization.
Enterprise AI agents are entering business applications faster than many security operations centers can monitor their behavior. Most detection systems still draw on endpoint, network, email, and identity signals, which may show individual transactions without explaining the business activity behind them. As autonomous agents spread across departments, security teams need visibility into their activity inside applications.
Vipin Varma is Senior Vice President, Chief Information Security Officer, and Head of Cybersecurity Practice at CitiusTech, where he oversees enterprise security and leads the company's customer-facing cybersecurity practice. His responsibilities include managing risks associated with internal AI initiatives and advising clients on cybersecurity challenges. He believes that organizations are adopting AI capabilities without sufficient visibility into the security threats they introduce.
“Everyone is talking about governing their agents, but where is the control plane that monitors an agent's behavior and reports it to the enterprise threat management function?” Varma says. Even with defined permissions and safeguards, agents can operate outside the SOC's visibility, adding to the monitoring burden as organizations deploy more of them.
The proliferation of AI agents is outpacing security oversight
Employees can now build agents for specific tasks with relatively little investment, while enterprises are developing customized agents for broader business applications. As these systems proliferate across departments, each with different owners and access requirements, security teams must manage risks associated with deployments they may not have helped design or implement.
Each deployment also requires safeguards that can be considerably more expensive than the agent itself. “The cost of securing an individual agent may be an order of magnitude greater than the cost of building it,” Varma says. Guardrails, testing, model hardening, and deployment controls all add work, particularly when organizations must apply them consistently across independent initiatives. After launch, security teams need to know which agents exist, what they access, and how to review their behavior.
That information isn't always reaching the people responsible for threat detection. In Varma’s experience, “many threat managers have no visibility into the AI initiatives and innovations happening in their organizations.” Even when security teams have an inventory of those initiatives, existing monitoring tools may still provide an incomplete view of agent activity.
AI-powered detection remains constrained by existing telemetry
Security vendors are introducing AI analysts, automated investigations, and incident response agents, but the systems supplying them with information have changed far less. Endpoints, networks, identity services, and email remain the primary telemetry sources for many SOCs. “You can keep adding AI agents to analyze existing signals, but those agents are still operating on today's sensors,” Varma says. This limitation becomes more pronounced when agents operate across business applications. A login or data transfer may appear routine in isolation, while understanding the sequence requires visibility into the workflow the agent is executing.
More sophisticated analysis of those events can’t recover context that monitoring systems never captured. Assessing connected actions taken autonomously requires visibility into application behavior alongside technical signals, including business logic that standard integrations don’t always expose.
Customized applications complicate AI agent monitoring
Enterprise applications pose a difficult monitoring challenge because of how extensively organizations customize them. “There's no standardized connector that gives you everything you need from SAP, an HR system, or Workday,” Varma says. Even widely used enterprise applications are heavily customized, requiring security teams to understand how individual business processes work before they can identify suspicious activity.
As AI agents operate across these environments, threat detection must account for how they access systems, move information, and interact with business applications. “The real value will come from bringing business intelligence, business logic, and business context into threat analysis, and expanding the scope of that analysis,” Varma says.
Security operations must evolve with agent deployment
Integrating new signals into the SOC requires decisions about ownership, monitoring parameters, and escalation. Security leaders must determine which agent activities warrant attention and what level of confidence is needed before automated systems take action. “In many cases, you don't want an automated block or mitigation decision without a person reviewing it,” Varma says.
Maintaining that human oversight requires experienced analysts, yet automation is increasingly taking over the routine Level 1 work through which practitioners develop their investigative skills. Varma sees a potential problem for the future security workforce. “You need fewer Level 1 analysts and many more experts because the person making the final judgment has to understand the context. Where will the pipeline of future experts come from?” he says.
The operational changes could take time that fast-moving AI initiatives don't allow. Varma warns that security functions may spend a year or two recognizing the monitoring gap, selecting solutions, and implementing them. “I think that will be too late,” he says. During that period, agents can continue spreading through applications and accumulating access to business information.
Agent deployment and security oversight should advance together
For enterprises deploying agents, visibility needs to be considered when applications and workflows are designed, with behavioral signals flowing into established threat management processes. Analysts must also understand the operational consequences of what they monitor. Delaying the work until agents are widely deployed leaves security teams trying to reconstruct behavior their systems were never equipped to observe. “You can't just throw an agent at the problem and hope for the best,” Varma concludes.