Exposure Resilience Helps CISOs Decide Which Vulnerabilities Matter As Exploit Windows Shrink
Sunil Varkey, EVP and CISO at Hexaware Technologies, explains why security teams should focus on the weaknesses attackers can reach and the context SOC agents need to act.
Make The Security Digest one of your go-to sources on Google


The vulnerability always existed, but the terrain changed. Now there are more people outside who know how to attack.
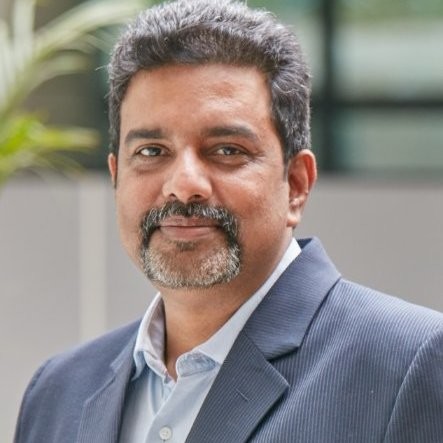
Sunil Varkey
AI is speeding up vulnerability discovery for defenders and attackers alike, and the time between disclosure and a working exploit is getting shorter. Patch cycles built around days or weeks of testing weren't designed for that pace, and not every vulnerability carries the same risk. Many security leaders now focus first on the weaknesses an attacker could reach and close off the path to them. That takes telemetry, identity, and exposure data viewed together, which AI agents in the SOC also need before they can safely act.
Sunil Varkey is the EVP and Chief Information Security Officer at Hexaware Technologies, a global IT services and consulting firm. Over more than 30 years in cybersecurity leadership across banking, telecom, IT services, and manufacturing, he has served as global CISO at Wipro and led cybersecurity assessment and testing at HSBC. Varkey makes the case that security teams should move from vulnerability management to exposure resilience, which means understanding which weaknesses an attacker can reach and how to cut off the routes to them.
"The vulnerability always existed, but the terrain changed. Now there are more people outside who know how to attack," Varkey says. For years, teams could leave low- and medium-severity flaws in older applications unpatched because exploiting them took time and skill. AI makes many of those flaws easier to exploit, so teams need to look again at risks they once considered safe to leave open.
Beyond the severity score
Security teams have traditionally decided what to fix first based on each vulnerability's severity score. A high CVSS rating meant patch it now, and a low one meant it could wait. Varkey says that score alone no longer tells teams how dangerous a flaw is. Whether an attacker can use it depends on who has access to the system, what privileges they hold, and how the system connects to the rest of the environment. "Now we are saying if it comes from an ID with a particular privilege, from this environment, and this sequence is followed, then we have a problem," he says.
Most teams aren't set up to see those conditions together. A typical system runs dozens of applications, and vulnerability teams usually review each flaw on its own, without looking at how flaws connect across those applications. Scanning tools tend to check one type of asset at a time, such as operating systems, applications, or network devices. As a result, information about identities, misconfigurations, and exposed systems sits in separate places. Exposure resilience means bringing that information together so teams can see whether an attacker could reach a given system.
That work starts with knowing what software the organization runs and where. In late 2021, security researchers disclosed a critical flaw in Log4j, a free, open-source logging tool built into thousands of applications. Log4j often sat inside other software, so many organizations had no list showing which of their systems used it. Without a software bill of materials, which records every component inside an application, teams had to search system by system. "We knew it was used heavily, but we never knew where it was used. There was no inventory of it, and that took most of the time," Varkey says.
Revisiting old permissions
When business teams rush new systems into production, security often takes a back seat. Accounts get elevated permissions to make testing easier, and those permissions frequently stay in place after launch. Users and service accounts end up with far more access than they need. Security leaders can see the risk but can't always remove access that other teams rely on, and Varkey says CISOs need backing from executives to clean it up. "You gave this privilege to a service account or an AI environment. Is that really needed? CISOs should be empowered to clean that environment up and reduce exposure," he says.
The first step is being able to trace every account and see what it's allowed to do. Each user, system, and service account should have only the access it needs. Teams also need to keep configurations in check and find old systems that are still on the network but no longer have an owner. Every one of these steps removes a route an attacker could use.
This also changes the vulnerability management team's job. The team has mostly focused on tracking flaws and making sure patches get applied. Now it also needs to watch accounts, permissions, system settings, and anything exposed to the internet, since each of these affects whether an attacker can get in. "Vulnerability management teams have to evolve into a bigger group that looks at attack surface management and identity exposures together, maybe an exposure resilience group," Varkey adds.
Where agents step in
AI agents in the SOC depend on that same combined view. Many identity tools pull data from directory services to flag over-privileged and inactive accounts. Varkey sees more value in pairing that identity data with telemetry from across the environment, which shows how those accounts behave day to day. "If I take the same data, put it into a large language model, and correlate it with my telemetry, I may get more insight," he says.
Teams decide how much freedom to give an agent based on the cost of a mistake. Varkey expects agents to start with routine tasks that entry-level analysts handle today. For example, if a user logs in from two distant cities within an hour, the account has likely been compromised. An agent can reset the password and log the user out of active sessions, just as an analyst would. If the agent is wrong, the impact is limited to one account.
Decisions with wider impact are harder to hand off. Shutting off access to a system that brings in revenue can disrupt the business, and weighing that tradeoff takes people who understand the company's priorities. "If my key revenue-generating application is exposed to the internet, am I going to immediately block it completely? I may not do that," Varkey says. Many teams design agent workflows with that line in mind. Automation handles contained responses, and a person approves anything that affects live business systems.
Varkey expects the industry to reach a point where faster patching can't keep up with how quickly AI uncovers new vulnerabilities. Teams that already know what systems they run and who can access them will be better prepared when that happens. "The current norm is not working. We need to go back to the drawing board and look at how we redesign this," he says.