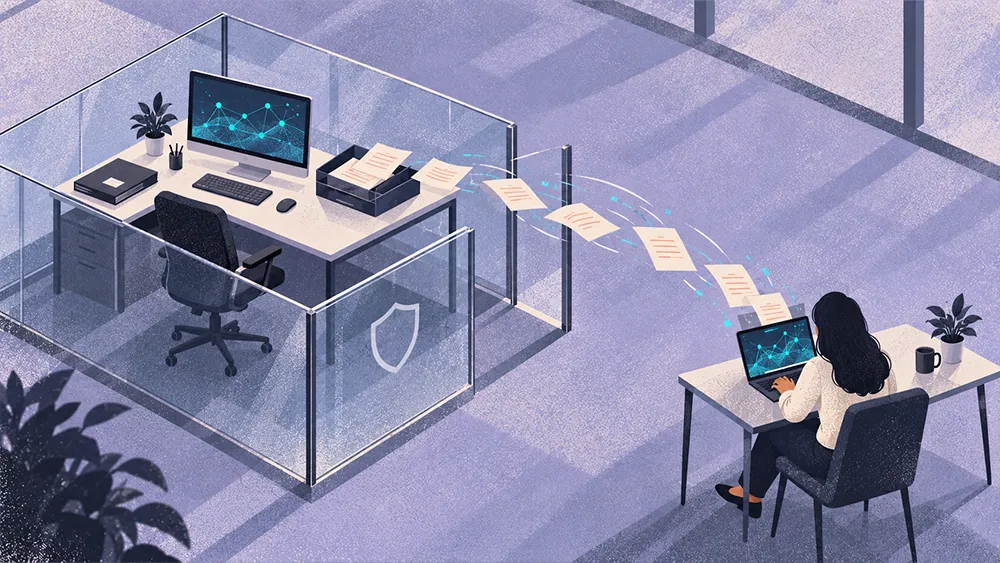
People tend to use the tools they're comfortable with, instead of the ones their organization provides.
 Nethusha RavisuthanSales Support & Operations Manager @ Microsoft
Companies can establish AI security policies and provide approved tools, but that doesn't mean employees will use them. More convenient alternatives can draw workers toward unauthorized tools, limiting visibility into how company data is handled. As AI becomes more embedded in enterprise operations, governance must account for employee behavior, system permissions, and oversight.
Nethusha Ravisuthan is a Sales Support & Operations Manager at Microsoft, where she works on enterprise product adoption and operational governance. She also lectures on AI security and governance and is developing a course on responsible AI and security for students in Sri Lanka.
"People tend to use the tools they're comfortable with, instead of the ones their organization provides," Ravisuthan says.
Employee preferences pose a threat to enterprise AI security policies
Ravisuthan identifies employee preferences as a source of shadow AI, where workers use AI services without organizational authorization, potentially exposing confidential information outside established security controls. "Let's say an organization gives employees access to Claude, but one employee is more familiar with ChatGPT and inputs confidential information into it. If ChatGPT were then compromised, the company's confidential information could be exposed," she explains.
Preventing unauthorized use requires more than prescribing an approved platform. Employees also need access to the capabilities they rely on, along with sufficient training to use them effectively. Similar concerns about access and authorization arise when enterprises deploy AI agents. Even within approved environments, organizations must determine what these systems can do and how to restrict their permissions.
AI agent permission limitations as a governance priority
An AI agent assigned to sales operations may require access to specific business systems, but excessive permissions could allow it to perform tasks beyond its intended function. "What if it has the capability to do things beyond sales that you haven't authorized or granted access to?" Ravisuthan says.
Drawing on her experience at Microsoft, she describes how organizations can restrict agents to defined responsibilities. "Without sharing confidential information, we have agents for sales, client analysis, market analysis, and so on. But we limit and tailor them to a specific range of activities," she says. Setting those restrictions also requires clear accountability, particularly when business teams and security specialists have different responsibilities for overseeing AI deployments.
Clear ownership and provider transparency strengthen AI oversight
Ravisuthan recommends assigning oversight according to an agent's purpose, with operational managers defining its responsibilities and security specialists advising on access restrictions. "If it's a sales agent, a sales manager needs to oversee it. If it's related to security, a cybersecurity expert should advise on when and how to limit access," she explains.
AI providers should explain how their systems enforce these restrictions so enterprise customers can establish appropriate internal controls. "These rules should be documented, and the enterprises providing the services should be transparent about them, rather than leaving all responsibility for regulation to the enterprises using the services," Ravisuthan says.
Employee training brings AI security policies into practice
While documented permissions help organizations govern autonomous systems, managing employee AI usage also requires continued education, especially as approved platforms introduce new features. Ravisuthan points to Microsoft's internal Copilot training as an example of how organizations can encourage employees to use approved technology instead of turning to familiar alternatives. "We can't just offer Copilot to users and expect them to adopt it automatically," she says. "They might prefer OpenAI tools or Claude."
Employees may not realize their approved tools already offer capabilities they're seeking elsewhere. "We held an event on Copilot last April, and even I learned how much more there is within Microsoft Copilot because we had an expert come in and train us," Ravisuthan says. She recommends regular training and dedicated teams to keep employees informed about new features and reduce reliance on unauthorized alternatives.
"When employees use the tools provided by the company, the organization can monitor their use and manage security more effectively," Ravisuthan concludes.